


Hot Games
Live Cards
Popular Games
Creating a Secure Fairplay Login
Everything downstream depends on how the account is created, so the first minutes deserve care. The registration flow — whether you arrived searching sign up my Fairplay login or simply opened the site — runs in five steps:
- Open the official site through a typed address or your own bookmark
- Choose Sign Up and register with your phone number, the primary identifier for Indian accounts, or with an email
- Set your fairplay login id — the username or number the account answers to
- Create a password that exists nowhere else: twelve characters or more, mixed, and stored in a password manager rather than memory
- Confirm the OTP that arrives by SMS, or the verification link by email
Two choices here decide most future problems. The phone number must be one that stays yours — OTP login and recovery both flow through it, so a borrowed or temporary SIM plants a time bomb under the account. And the password must be genuinely unique: reused passwords are how a leak on some unrelated forum becomes a drained betting balance, because attackers test stolen pairs everywhere.
What a strong setup looks like in practice:
- A fairplay login id you can state without embarrassment, since it is not a secret
- A password no other service has ever seen, living in a manager
- A SIM that stays in your phone and your name
- Recovery email checked recently enough that you remember its own password
The id alone opens nothing; the combination of id, password, and phone is the whole perimeter — build each piece properly once.
Managing Account Settings
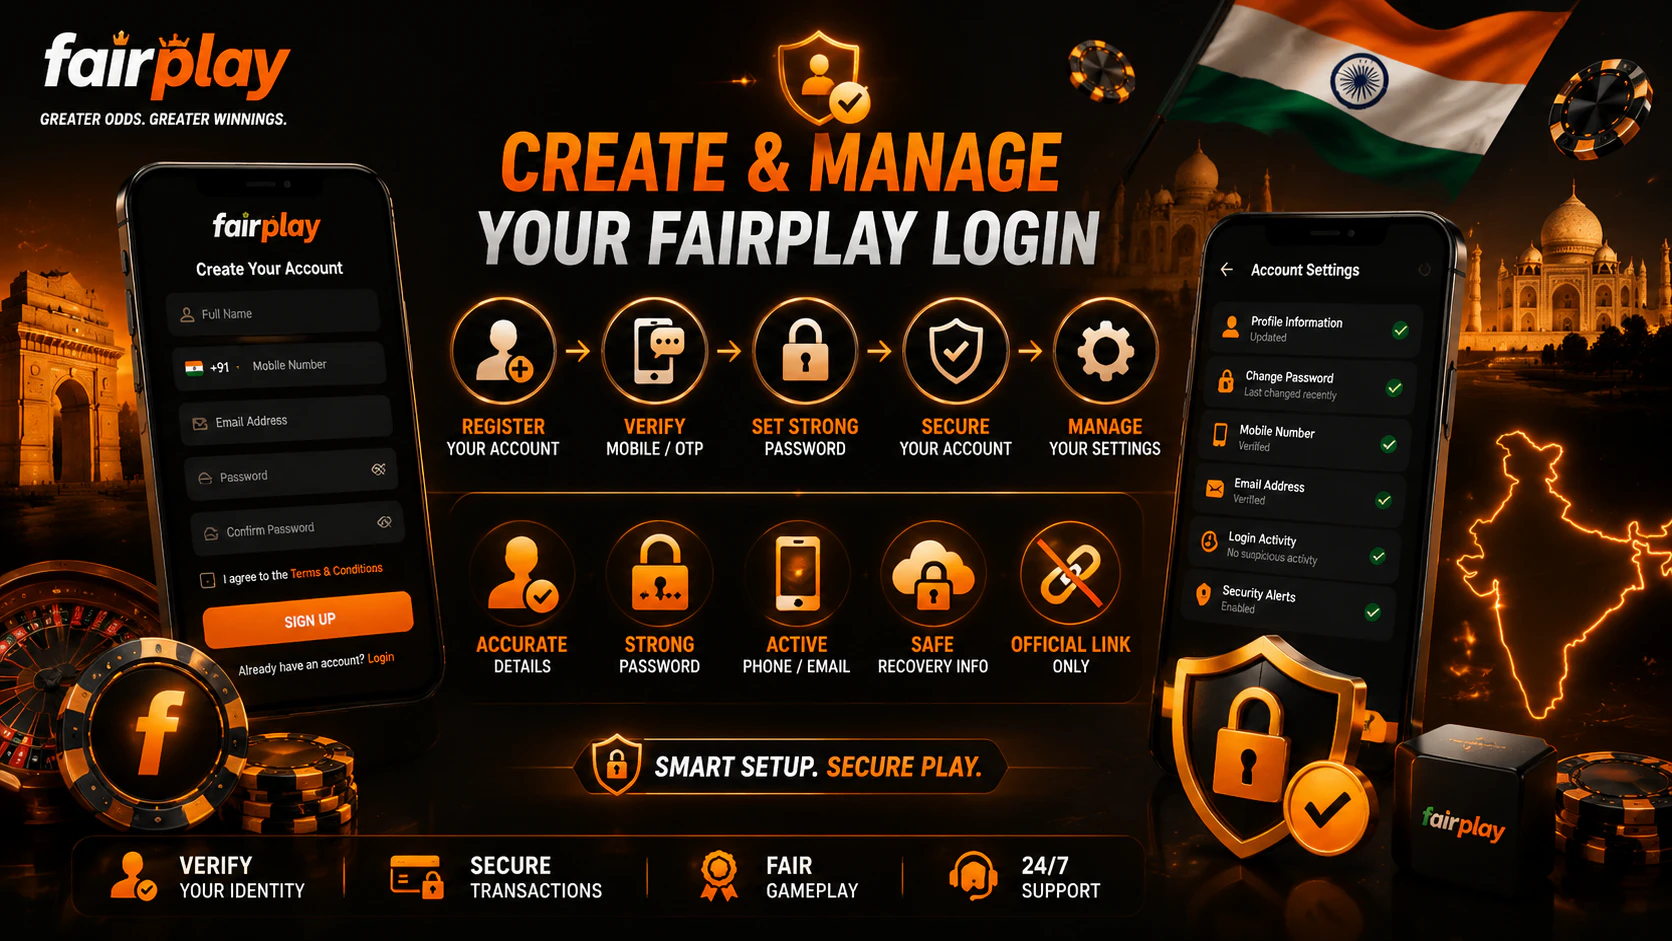
The security section of the account is worth a visit right after registration, not after an incident. Four settings carry the weight:
| Setting | What to do | Why it matters |
| Password | Change it if there is any doubt about its uniqueness | The first factor is only as good as its secrecy |
| Phone and email | Confirm both are current and accessible | Recovery and OTP depend on them entirely |
| Device and session list | Review where shown; end unfamiliar sessions | Old sessions on old phones are open doors |
| OTP behaviour | Know which actions trigger codes | A code arriving unrequested is a warning, not noise |
The session review deserves a habit: once a month, open the list where the platform shows it, and close everything you do not recognise — the phone you sold, the browser at a friend’s place, the session from a city you have not visited. An unexpected OTP deserves the opposite of habit: full attention, because someone just tried your number at the login form. The right response is changing the password, not deleting the SMS.
Common Fairplay Login Problems
Login failures cluster into a few patterns, each with a fix:
| Problem | Likely cause | What to do |
| Wrong password error | Typo, caps lock, or an old password remembered | Retype slowly; use the manager’s stored value; reset if unsure |
| OTP not arriving | Network delay, DND filters, wrong number | Wait two minutes, check signal, re-request once; verify the number |
| OTP rejected | Expired code or mistyped digits | Request a fresh code; enter within its validity window |
| Account temporarily blocked | Too many failed attempts or a security flag | Pause, then use recovery; contact support through the official site |
| Page will not load the form | Browser cache, extensions, or an outdated app | Clear cache, try a private window or another browser, update the app |
| Logged out repeatedly | Cookie settings or aggressive cleaners | Allow cookies for the site; whitelist it in cleaning tools |
One meta-rule sits above the table, and it matters more than any single row: never solve a login problem by hunting for an alternative site that “works”. The brand appears under several names — fairplay 24, fairplay pro, my fairplay among them — and that multiplicity is exactly what clone-builders exploit. A login failure is fixed inside the official page or through recovery, not by typing credentials into the next lookalike a search engine offers.
Recovering a Fairplay Account
Recovery exists for the day the password is gone or the account misbehaves, and it works best when prepared in advance. The standard route: open the login form, choose the forgotten-password or recovery option, identify yourself by the registered phone or email, receive the OTP or reset link, and set a new password — unique again, into the manager again. With access to the registered phone, the whole loop takes minutes, and practising it once on a calm day — just to see the screens — makes the stressed-day version routine.
Without that access, the path narrows to support through the official site, and the questions get appropriately harder: details about the account, its history, and where possible its transactions. That is friction by design — the same difficulty that slows you protects the account from a stranger claiming to be you. Two situations call for recovery even when login still works: any suspicion the password leaked, and any sign of activity you do not recognise — bets you did not place, settings changed, sessions from nowhere. In both cases the order is fixed: change the password first, end all other sessions where the settings allow it, then review what happened. A compromised account with a fresh password and closed sessions is a contained incident; the same account left “to watch for a while” is an open one.
Protecting Against Phishing and Fake Sites
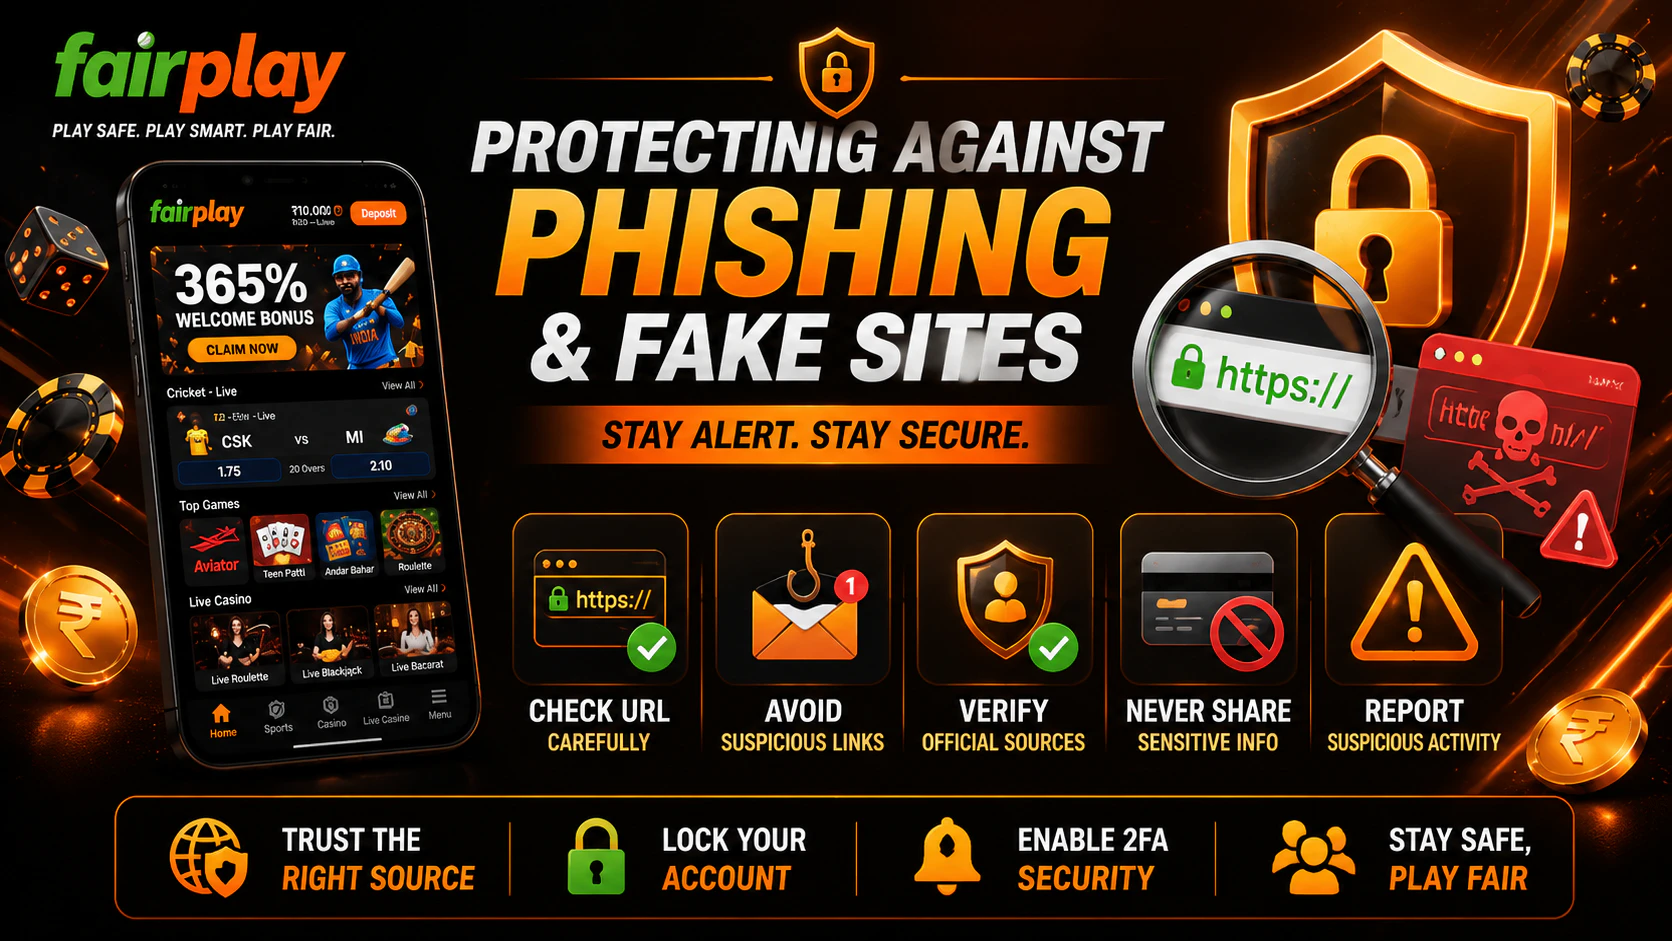
The brand’s name variants and rotating domains create perfect cover for fakes, so domain literacy is the core skill of this entire page. A counterfeit login page does not look suspicious — it looks identical, because copying a design takes an afternoon. What it cannot copy is the address, and that is where the check lives:
- Read the domain character by character before typing anything; one swapped letter is the whole trick
- Confirm the connection is secure and the certificate matches the domain
- Arrive by your own bookmark or typed address — never through ads, search shortcuts, forum links, or anything forwarded in WhatsApp and Telegram
- Treat “new official domain” announcements in chats as hostile until the official site itself confirms them
- Cross-check the footer: the licence details belong there, and their absence on a login page is a loud signal
The messenger point earns emphasis for India specifically: forwarded “working links” are the dominant local delivery route for clones, often dressed as helpful updates when a domain changes. The safe response to any domain confusion is the same — go back to the address you have verified before, or verify fresh through the footer and official channels, and only then log in. Thirty seconds of reading an address bar is the entire price of immunity, and it is the same thirty seconds whether the search that brought you arrived as fairplay login, fairplay 24 login, or fairplay pro login — the names vary, the check does not.
Two-Factor Authentication Setup
Two-factor authentication is the strongest upgrade a login can get: even a stolen password fails without the second code. On Fairplay the honest picture has a caveat — the built-in 2FA option, typically via Google Authenticator, is offered on some versions of the platform and absent on others. So the instruction is conditional by necessity: open the account’s security settings, and where the platform offers 2FA, enable it without hesitation — link the authenticator Fairplay App, store the backup codes somewhere offline, and from then on logins ask for the rotating six-digit code alongside the password.
Where the option is absent, the compensating controls are the ones this guide already covers, applied strictly: a genuinely unique password, a protected SIM, OTP discipline — codes typed only into the page you navigated to yourself, never read out or forwarded to anyone — and regular session reviews. And one universal rule regardless of 2FA status: no legitimate process ever requires telling a code to a person. A caller, a chat “support agent”, a message asking for the OTP “to verify your account” is the attack itself, mid-execution. The code goes into the form, or it goes nowhere.